In September 2026, a report from the U.S. Federal Reserve's Inspector General revealed a cybersecurity lapse. A former Federal Reserve employee had been flagged multiple times for handling confidential information in ways that violated established security procedures—including copying sensitive files to unencrypted USB drives and attempting to send confidential information to personal email accounts. The employee was eventually flagged again just before retirement, but the Inspector General found that the organization's response to the repeated warnings insufficient.
The incident is a useful reminder that insider risk is not always about a disgruntled employee deliberately trying to damage an organization. Sometimes it is about excessive access, poor processes, inadequate monitoring, human error and failures to act when warning signs appear.
And for today’s organizations, the risk is expanding.
Employees, contractors, vendors, partners, and even executives can create serious security exposure through malicious intent, compromised credentials or simple mistakes. The growth of cloud platforms, remote work, third-party applications and AI tools has also made the traditional corporate perimeter blurred beyond recognition.
To Wipe Out Threats, Contact us at: hello@taas1.com.
For CXOs, the question is therefore no longer simply:
“How do we keep attackers out?”
It is:
“Who has access to our critical information, how is that access being used, and would we know if something went wrong?”
Insider risk isn’t just an IT concern — it’s a leadership blind spot.
The 6 Faces of Insider Threats
Insider threats are not one-size-fits-all. They can be intentional or accidental, obvious or difficult to detect. Understanding the different forms they can take is the first step toward reducing exposure.
-
Data Theft
Data theft occurs when someone within an organization exfiltrates or misuses sensitive information without authorization. This could include customer records, financial information, intellectual property, confidential contracts, employee information or business strategies. Sensitive data often leaves through personal emails, external drives, or unauthorized cloud apps. For a business, the consequences can extend well beyond the loss of information. Regulatory penalties, contractual consequences, reputational damage and loss of customer trust can follow.
-
Sabotage
Sabotage occurs when someone deliberately damages, disrupts or destroys business systems or information. A disgruntled employee, contractor or compromised insider account could delete critical files, disrupt systems, introduce malicious software or interfere with business operations.
For executives, the important question is not simply, “Can someone cause damage?” It is “How quickly can we detect the damage and restore operations?” This is where resilient infrastructure, tested backups and a well-defined recovery strategy become essential.
-
Unauthorized Access
Not everyone who can technically access information should be able to access it. For instance, a former project manager retaining admin rights long after moving departments.
Unauthorized access occurs when an individual obtains information or enters systems beyond what their role requires. Sometimes this is deliberate. In other cases, excessive permissions simply remain in place after an employee changes roles or responsibilities.
This is why access management cannot be a one-time exercise. Privileges should be reviewed regularly and adjusted as roles change.
The principle should be straightforward: people should have access to what they need—not everything they could potentially access.
-
Negligence and Human Error
Not every insider threat involves malicious intent. An employee may accidentally send confidential information to the wrong recipient, download a malicious attachment, misconfigure a cloud service, use an insecure device or ignore an established security procedure.
From a CXO perspective, this distinction is important. Security must anticipate human error, not rely on perfect behavior.
Organizations need processes, technology and controls that reduce the consequences of inevitable human mistakes.
-
Credential Sharing
When employees share passwords with colleagues, contractors or others, organizations lose visibility into who is actually accessing their systems.
Credential sharing can make it difficult to identify the individual behind suspicious activity and can allow compromised credentials to move laterally across systems. Once credentials circulate informally, accountability evaporates.
Strong password policies, multi-factor authentication and appropriate identity and access controls can significantly reduce this risk.
-
Unauthorized AI Use
Employees may turn to public or unapproved AI applications to summarize documents, analyze data, write code or perform everyday business tasks. The problem arises when sensitive company, customer or proprietary information is entered into a tool that has not been evaluated or approved by the organization.
The issue is not whether employees should use AI.
The strategic question is how the organization can enable AI productivity without losing control of sensitive information.
CXOs need clear AI governance policies covering approved tools, acceptable use, sensitive data and accountability.
Spotting the Red Flags
Insider threats rarely announce themselves.
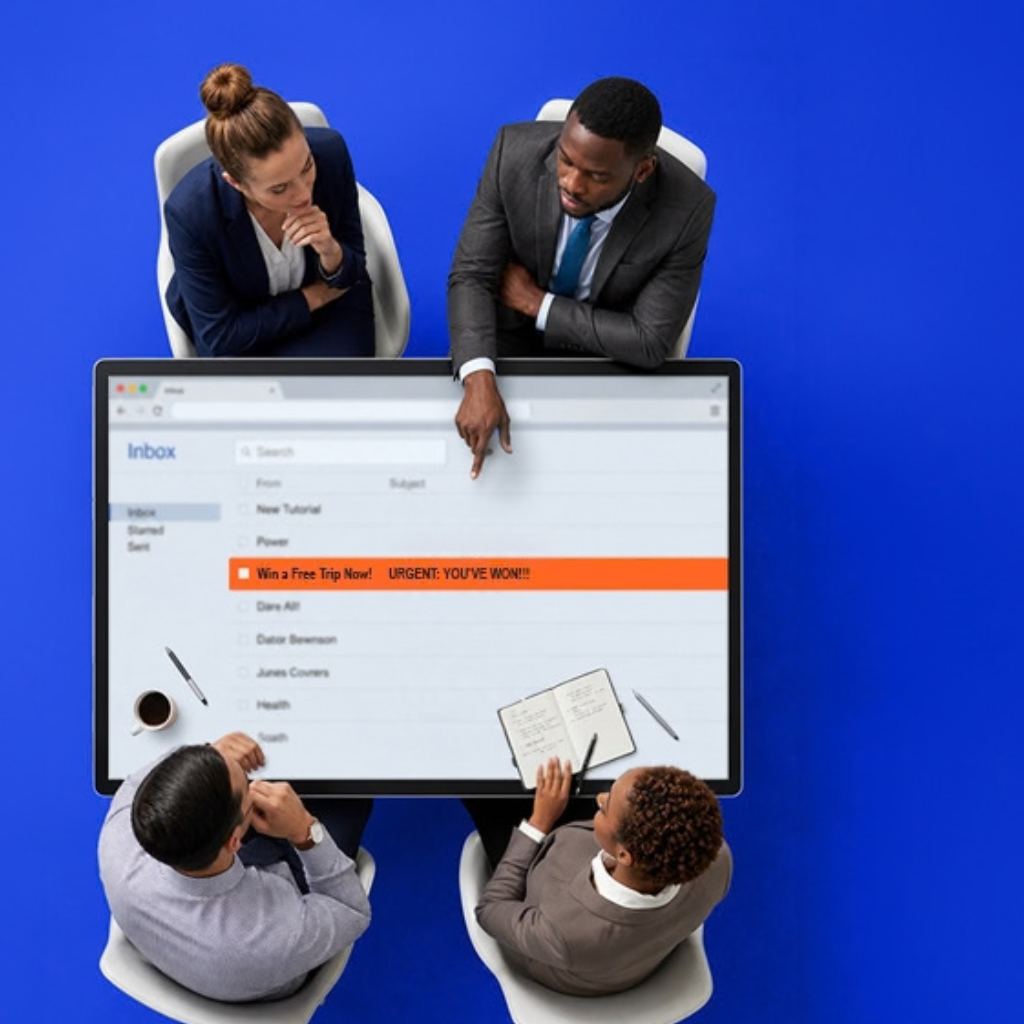
Security teams should therefore look for patterns and anomalies rather than relying on a single suspicious event.
Some indicators include:
- Unusual access patterns: An employee suddenly accesses confidential information unrelated to their role.
- Excessive data transfers: Large volumes of customer or company data are downloaded or moved to external storage.
Repeated authorization requests: Someone repeatedly seeks access to business-critical systems without a clear business requirement.
- Use of unapproved devices: Confidential information is accessed through personal or unauthorized devices.
- Disabling security controls: Antivirus, endpoint protection or other security mechanisms are deliberately disabled.
- Unapproved AI usage: Employees enter confidential or proprietary information into public AI platforms that have not been approved by the organization.
- Unusual behavioral patterns: Significant changes in work patterns, system usage or interactions with sensitive information may warrant further investigation.
None of these indicators, on its own, proves malicious activity. But together, they form a behavioral fingerprint worth investigating. The objective is not to monitor employees indiscriminately. It is to establish sufficient visibility to identify genuine risks while maintaining appropriate privacy and governance.
For leadership teams, the key is context, consistency and timely response.
Building Your Defenses From the Inside Out
Reducing insider risk requires more than a security product. It requires a coordinated framework involving people, processes and technology.
- Strengthen Identity and Access Controls
Implement strong password policies and multi-factor authentication wherever possible. Review privileged accounts regularly and remove unnecessary access.
- Apply Least-Privilege Access
Employees should have access only to the systems and information required for their responsibilities. Access should be reviewed when employees change roles and immediately when they leave the organization.
- Establish Clear Security and AI Policies
Employees need practical guidance on protecting sensitive information, using company systems, sharing data and working with AI tools.
Policies should be supported by regular training—not simply acknowledged once and forgotten.
- Build Resilience Through Backups
Even the strongest security controls cannot eliminate every risk.
Regular, protected and tested backups can help organizations recover from accidental deletion, sabotage, ransomware and other disruptive incidents. Backups are meaningless unless recovery is proven.
- Prepare for the Incident Before It Happens
Every organization should have an incident response plan that clearly defines responsibilities, escalation procedures, communication protocols and recovery priorities.
When an incident occurs, the first few hours can be critical. A documented plan helps leadership teams move from uncertainty to coordinated action.
Insider Risk Is a Business Leadership Issue
Cybersecurity is often viewed as a technology challenge. Insider risk demonstrates why that view is incomplete.
The real issue is business continuity, customer trust, intellectual property, regulatory exposure and operational resilience.
A strong security strategy therefore needs to answer some fundamental questions:
Who has access to our critical information?
- Are we able to identify unusual activity?
- How quickly would we know if sensitive data were being misused?
- Could we recover if a critical system or data set were deliberately or accidentally compromised?
- Do our employees understand how they can use AI without creating unacceptable business risk?
If the answers aren’t clear, there may be gaps worth addressing.
Don’t Fight Internal Threats Alone
Protecting your organization from insider risk can be challenging, particularly as IT environments become more distributed and employees use an increasing number of cloud, SaaS and AI platforms.
An experienced IT and security partner can help you build the visibility, access controls, monitoring, backup strategy and incident response capabilities needed to strengthen your security posture.
The goal is not to create an environment where employees are treated as potential attackers. It is to build an organization where trust is supported by appropriate controls, access is governed intelligently, unusual activity is visible, and the business is prepared to respond when something goes wrong. Because cybersecurity is not only about keeping threats out.
It is about protecting your business from the inside out.
Ready to understand where your organization may be exposed? Schedule a 10-minute discovery call to discuss your current security posture, identify potential gaps and explore practical ways to strengthen your defenses.